01
Third-Party Risk Management Orchestrator
Serverless AWS prototype that accepts vendor intake through Slack, applies configurable and explainable risk scoring, stores assessments in DynamoDB, and routes high-risk vendors to human review.
Joshua, in Hebrew
GRC engineer building secure, auditable systems that turn complex risk into decisive action.
[ 01 / SELECTED WORK ]
Recent public engineering evidence leads this portfolio, followed by completed security labs and early-stage product work.
[ PUBLIC ENGINEERING EVIDENCE ]
RECENT / OPEN REPOSITORIESServerless AWS prototype that accepts vendor intake through Slack, applies configurable and explainable risk scoring, stores assessments in DynamoDB, and routes high-risk vendors to human review.
Terraform lab provisioning an immutable, encrypted AWS S3 evidence vault with Object Lock, KMS, control mapping, and runtime evidence requirements for HITRUST-aligned assurance.
Working repository that turns Terraform deployments into verifiable audit evidence through compliant S3 primitives, automated capture, SHA-256 manifests, and immutable storage.
[ FOUNDATIONAL SECURITY LABS ]
COMPLETED / 2022Created a cloud SIEM, integrated Azure telemetry, and wrote KQL detections to map the origin of live attacks.
Built a controlled social-engineering simulation to demonstrate credential-capture risk and the human layer of security.
Configured a Windows Server environment and automated more than 1,000 user accounts with PowerShell.
[ CURRENTLY BUILDING ]
EARLY-STAGE PRODUCT WORKBuilding a security-first SaaS platform at the intersection of governance, assurance, and intelligent workflows.
Developing a fintech platform designed around clarity, trust, and responsible financial infrastructure.
[ 02 / OPERATING SYSTEM ]
Designing controls, evidence workflows, and governance systems that teams can actually operate.
Building detection workflows and investigating hostile activity across Azure environments.
Assessing controls through ISO 27001, ISO 42001, and industry practice.
Moving comfortably between KQL, PowerShell automation, identity, and infrastructure.
[ 03 / CREDENTIAL VAULT ]
Certified Information Systems Security Professional
Certified Lead Auditor · Certified Internal Auditor
Certified Lead Auditor · AI Management Systems
ISC2 Systems Security Certified Practitioner
Security+ · PenTest+ · Network+ · A+ · Project+
AXELOS IT Service Management
[ 04 / ABOUT JOSH ]
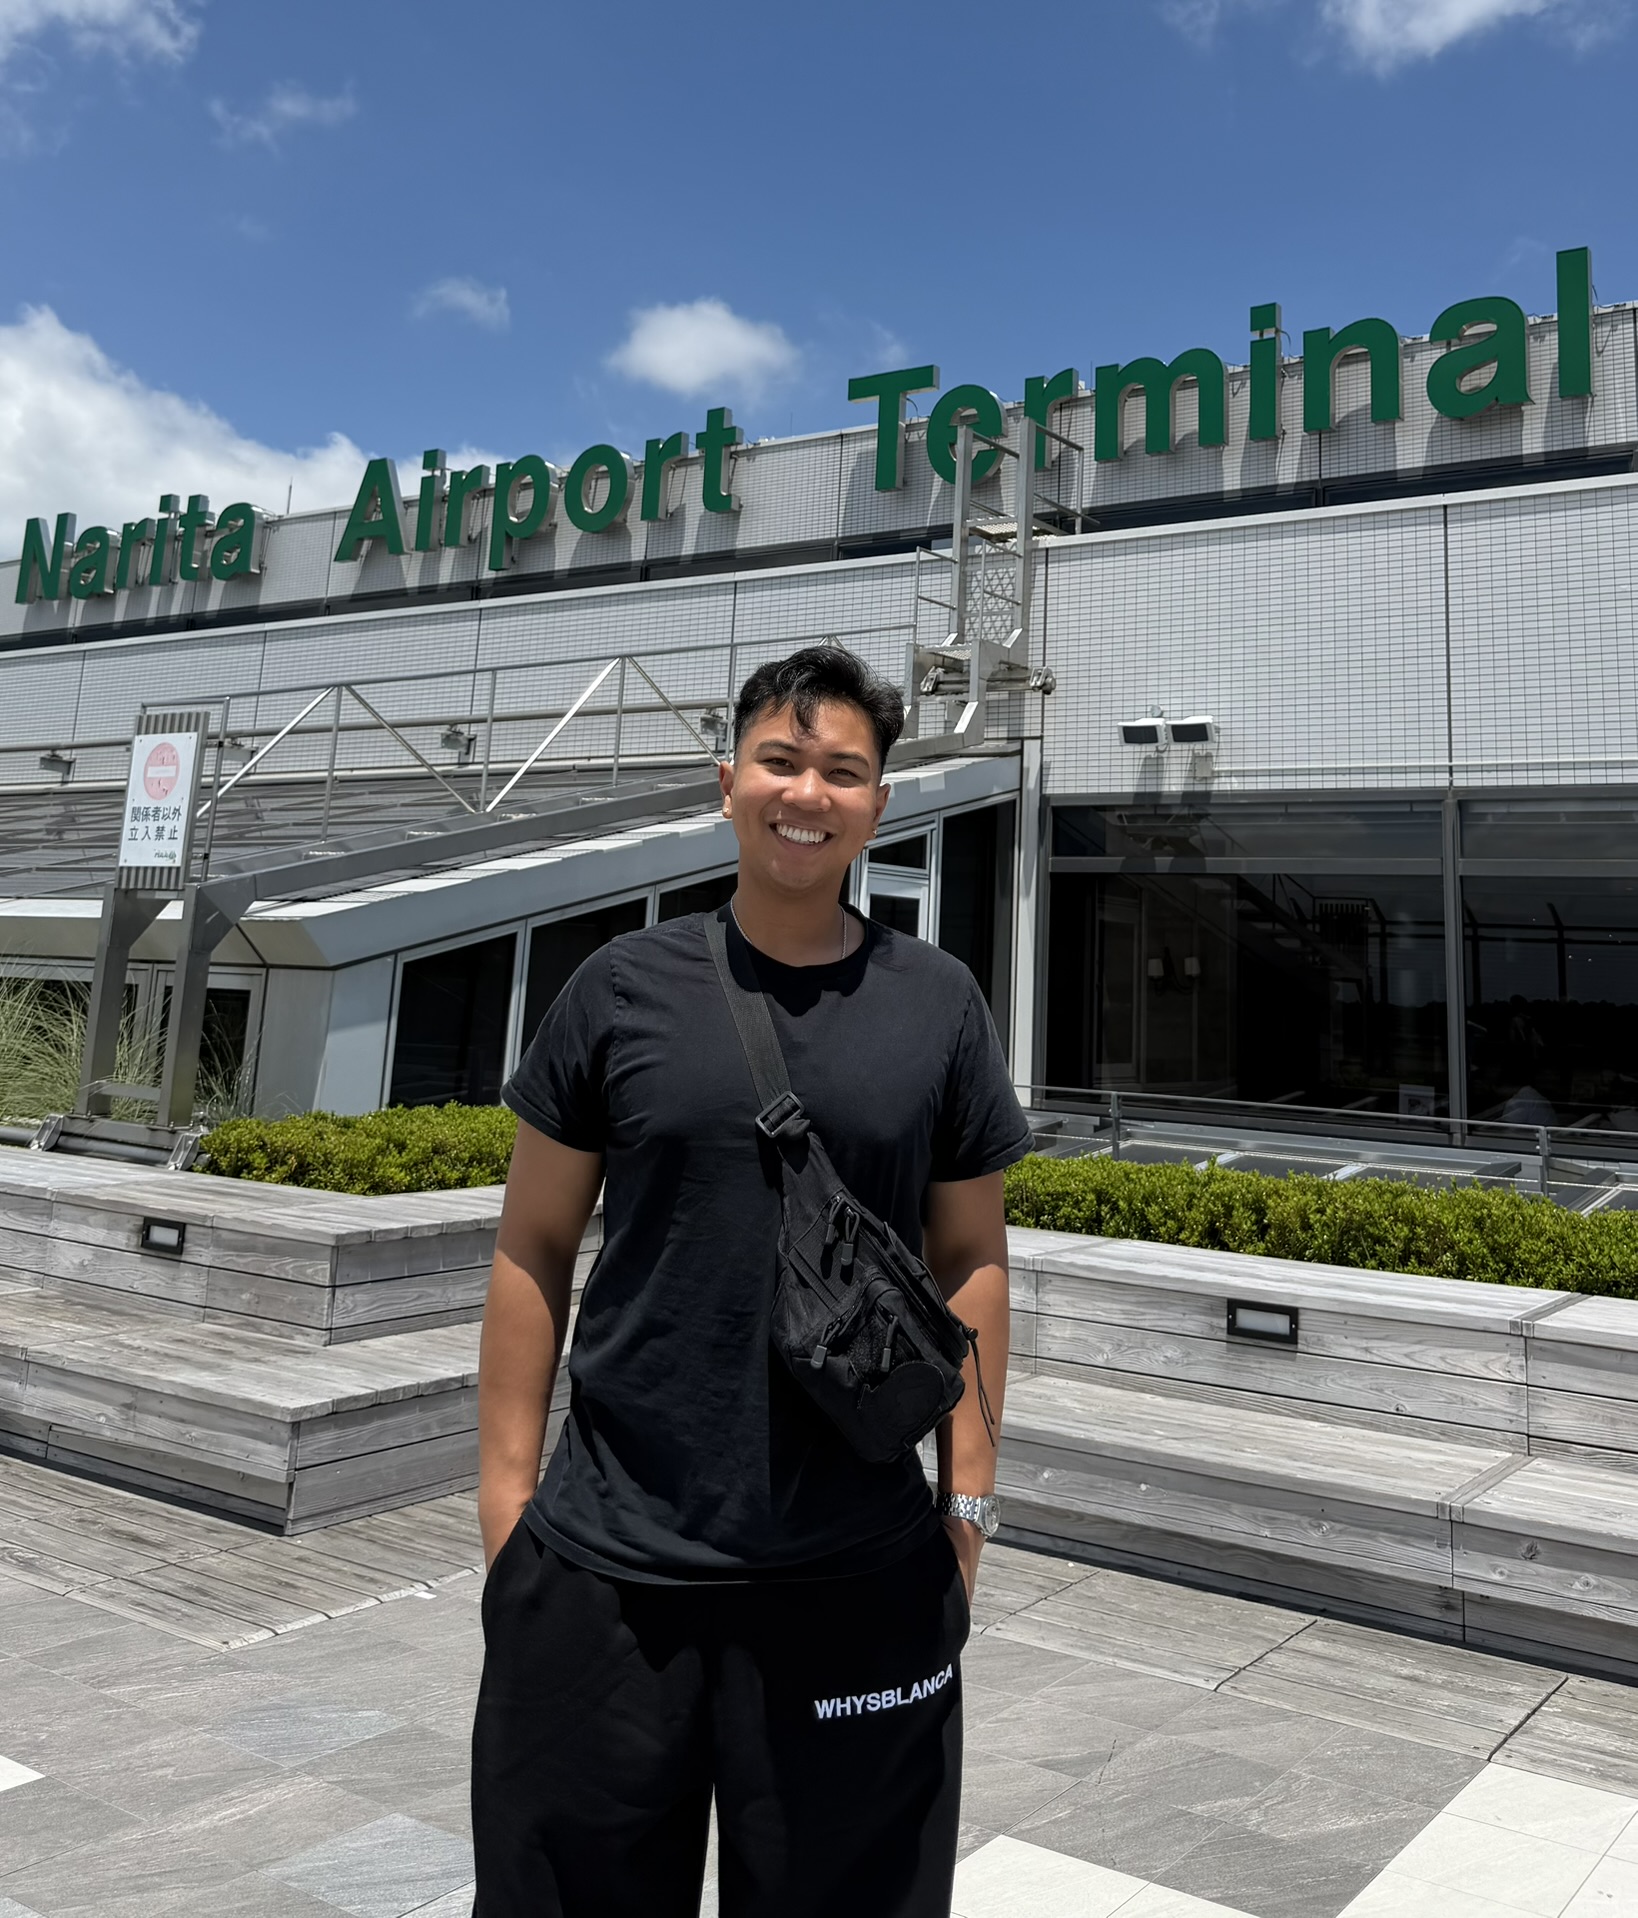
I'm a cybersecurity professional focused on information assurance. I began my career in incident response, identity and access management, systems administration, and audit support. That foundation led me toward GRC and eventually to Lead Auditor credentials across ISO 42001, ISO 27001, and ISO 27701. Today, I'm building compliance automation with AI tools.
Outside work, I like finding favorite restaurants with my wife, playing basketball, and lifting. I'm a try-hard at Battlefront 2, Battlefield 6, and Call of Duty, and I try to live by "work hard, play hard." Current goals: improve at golf, become a stronger swimmer and runner, and dunk on a 10-foot rim.